Remote Desktop Security Checklist for Small Business: 10 Essential Checks
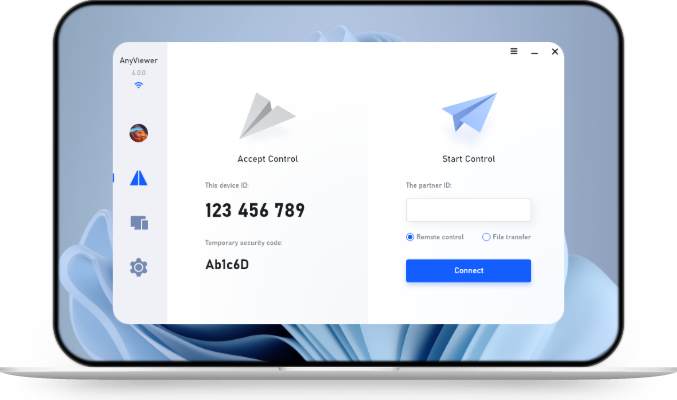
Unprotected RDP access and unmanaged accounts put business data at risk. This checklist covers closing direct RDP ports, enforcing MFA, and controlling session privileges. Learn how AnyViewer delivers ECC 256-bit encrypted remote access and central team management to simplify compliance.
By Ellie / Updated on October 8, 2026


What Is a Remote Desktop Security Checklist for Small Business?
A remote desktop security checklist is a repeatable set of controls for deciding who can connect, which devices they can reach, and how access is monitored and revoked. It covers both connection security and the computers at each end.
Traditional Windows Remote Desktop Protocol (RDP) and modern remote access applications handle connectivity differently. While traditional RDP requires complex network configurations and manual hardening, modern remote desktop solutions like AnyViewer combine enterprise-grade security controls, end-to-end encryption, and seamless deployment into a single, cost-effective platform.
Benefits of Using a Remote Desktop Security Checklist
Implementing a structured remote desktop security checklist helps small businesses establish strong access controls while keeping daily operations smooth and manageable. Key advantages include:
- Reduce avoidable exposure from public services and unused accounts.
- Give employees a consistent way to request and use remote access.
- Make offboarding easier by recording users, devices, and permissions.
- Improve recovery readiness by testing backups before an incident.
A completed checklist records evidence. Selecting a tool alone does not prove access is controlled, pairing proven security controls with an intuitive, manageable tool like AnyViewer ensures full compliance and ease of execution.
How to Secure Remote Desktop Access in 10 Steps
1. Inventory Every Remote Access Route
List office PCs, remote users, installed support tools, VPNs, and external contractors. Record a business owner and purpose for each connection, removing unapproved software and disabling unused services.
- The Check: Compare the approved list against installed applications and firewall rules. Investigate any unauthorized connection route.
- The AnyViewer Advantage: With AnyViewer Enterprise, IT administrators gain a centralized Management Center to monitor all company-linked devices, manage employee accounts, and enforce unified access policies from a single dashboard.
2. Remove Public RDP Exposure
Do not forward internet traffic directly to an office PC’s RDP port (normally TCP 3389). Exposing RDP directly to the web invites automated brute-force attacks and ransomware exploits.
- The Check: Ask your IT provider to verify externally that direct RDP ports are closed. Joint CISA/FBI StopRansomware advisories strongly warn against public RDP exposure.
- The AnyViewer Advantage: AnyViewer eliminates the need for port forwarding or exposed RDP ports entirely. Sessions are routed through secure, cloud-assisted architecture protected by Elliptic Curve Cryptography (ECC) 256-bit end-to-end encryption.
3. Require MFA and Individual Accounts
Assign each employee a unique account and strong password. Enforce multi-factor authentication (MFA / 2FA) across all remote entry points and protect recovery email channels.
- The Check: Test new-device logins to ensure saved credentials cannot bypass multi-factor authentication requirements.
- The AnyViewer Advantage: AnyViewer supports Account-Level Two-Factor Authentication (2FA) via verification codes to protect user accounts from unauthorized logins on untrusted devices.
4. Limit Permissions and Reachable Devices
Enforce the Principle of Least Privilege. Staff should only access assigned office PCs required for their specific work roles. Separate standard user accounts from administrative maintenance credentials.
- The Check: Verify that a standard employee account cannot access unassigned computers or execute administrative tasks.
- The AnyViewer Advantage: AnyViewer allows admins to group endpoints, assign explicit device permissions, and prevent unauthorized horizontal movement across your network.
5. Patch and Protect Both Endpoints
Keep operating systems, remote software, web browsers, and network hardware updated. Deploy endpoint protection, enable full-disk encryption, and set auto-screen locking on remote endpoints.
- The Check: Review security patch status and active antivirus alerts on both local and remote machines.
- The AnyViewer Advantage: AnyViewer frequently updates its core application to maintain high security standards and seamless OS compatibility across Windows, iOS, and Android.
6. Keep RDP NLA Enabled
If your organization still relies on legacy Windows RDP internally, ensure Network Level Authentication (NLA) is strictly enabled to authenticate users before establishing a session.
- The Check: Confirm the NLA requirement on every internal RDP host. Never disable NLA as a shortcut for connection troubles.
7. Restrict Unattended Access and Protect On-Site Screens
Use attended approval for temporary support sessions. Enable unattended remote access only for documented, authorized devices. Restrict clipboard sharing, drive redirection, and file transfers where unnecessary.
- The Check: End a test connection and confirm the remote computer immediately locks. Verify that prohibited file transfers fail.
- The AnyViewer Advantage (Privacy Mode): Working remotely can expose sensitive data on office monitors to on-site passersby. AnyViewer’s Privacy Mode allows users to black out the remote PC screen and disable its physical keyboard and mouse during a session.
8. Review Logs and Investigate Unexpected Sessions
Collect authentication logs to spot repeated login failures, connections from unusual geolocations, or activity outside normal business hours.
- The Check: Perform a test connection and locate its precise timestamp, user ID, and target machine in your access logs.
- The AnyViewer Advantage: AnyViewer logs session histories, device connection events, and administrative activities in the Management Center, giving IT managers full visibility over remote work activity.
9. Test Backups and Disaster Recovery
Maintain isolated, immutable backup copies disconnected from primary user networks. Periodically restore sample business files to verify integrity.
- The Check: Record backup restoration test results. Keep a written incident response plan with clear instructions on revoking remote access during a suspected breach.
10. Revoke Access Immediately Upon Offboarding
When an employee or contractor leaves, immediately disable their accounts, remove device pairings, terminate active sessions, and rotate shared secrets.
- The Check: Attempt to reconnect using a deactivated user account to confirm access revocation is fully effective.
- The AnyViewer Advantage: With AnyViewer’s centralized console, admins can unassign or remove a user from the corporate account in a single click, instantly cutting off access to all linked company endpoints.
Comparison: Traditional RDP vs. VPN vs. AnyViewer
|
Security & Feature Metric |
Traditional Windows RDP |
VPN + RDP Setup |
AnyViewer Remote Access |
|
Public Port Exposure |
High Risk (Port 3389 open) |
Low (Protected by VPN) |
Zero Port Forwarding Needed |
|
Encryption Standard |
Varies / Configurable |
IPSec / OpenVPN |
ECC 256-bit Bank-Grade Encryption |
|
Setup Complexity |
Complex (Firewall/Router setup) |
High (Server & Client config) |
Ultra-Simple (Install & Connect) |
|
Screen Privacy Controls |
None (Screen remains visible) |
None |
Privacy Mode (Blackout Remote Screen) |
|
Centralized Admin Console |
Requires Active Directory |
Requires VPN Gateway |
Built-in Cloud Management Center |
|
Cost Efficiency |
Requires Windows Pro/Server |
High Licensing & HW Costs |
Free Tier & Affordable Business Plans |
A Practical Review Schedule for a Small Team
Use this suggested schedule as a starting point. Increase review frequency when risk or contractual requirements demand it.
|
When |
Suggested owner |
Evidence to retain |
|
Before access begins |
IT provider |
Approved device, MFA test, permissions |
|
Weekly |
IT contact |
Reviewed alerts and unresolved updates |
|
Monthly |
Business owner and IT |
Access review and sample restore result |
|
Immediately after departure |
Manager and IT |
Revocation record and failed reconnection |
Why AnyViewer is the Ultimate Choice for Small Business Remote Access
AnyViewer simplifies secure remote desktop access for small businesses without the cost and headaches of traditional VPN or RDP configurations. Whether you need occasional attended IT support or permanent unattended access to office workstations, AnyViewer delivers complete peace of mind:
- Bank-Grade Security: Powered by 256-bit ECC encryption to prevent eavesdropping and data tampering.
- Privacy Mode: Work on confidential files without exposing your remote screen to anyone in the office.
- High-Speed Performance: Experience ultra-fast frame rates and rapid file transfers between endpoints.
- Scalable Business Licensing: Flexible plans designed for single power users, growing teams, and enterprise IT departments.
Choose the Right AnyViewer Plan for Your Business
1. AnyViewer Solo — Ideal for Freelancers & Remote Professionals
Fast, secure single-user remote access to your dedicated workstation.
- Key Features: High-speed connections, Privacy Mode (screen blackout), multi-monitor support, and large file transfers up to 1 TB.
- Best For: Freelancers, accountants, and remote employees accessing assigned office PCs.
2. AnyViewer Team — Built for Small Businesses & IT Support
Seamless multi-user coordination and centralized device management.
- Key Features: Multi-user licensing, custom device grouping, 9-screen wall monitoring, and mass unattended access deployment.
- Best For: Growing SMBs, helpdesks, and internal IT support teams.
3. AnyViewer Enterprise — Designed for Mid-to-Large Organizations
Advanced security controls, scalable deployment, and full compliance auditing.
- Key Features: Custom role and permission management, silent script deployment, 24-screen wall monitoring, and comprehensive audit logging.
- Best For: Managed Service Providers (MSPs), IT departments, and security-focused enterprises.
Conclusion
Protecting your business files doesn't require a massive IT budget or complex network overhauls. By implementing this 10-step security checklist alongside AnyViewer, you can empower your team to work securely from anywhere.
Ready to secure your remote workforce? Try AnyViewer free or view AnyViewer pricing plans to unlock advanced features like Privacy Mode and centralized team management.
 as a preferred
source on Google